Headlines from trusted publishers worldwide, collected automatically. We have not verified these stories ourselves: every headline links to its original source. Our own reporting is on the front page.
European and Ecuadorian cooperation leads to 20 arrests in major hit against drug trafficking
The operation, codenamed Operation CANTABRIA, underscores the success of strong cooperation between European and Ecuadorian law enforcement agencies, proving that joint efforts are key to tackling transnational criminal networks.Magnus BrunnerEU Commissioner f
Almost 50 arrested as police target Western Balkan network linked to killings
Nearly 50 suspects have been arrested in an international operation targeting a drug trafficking network with Western Balkan members, linked to killings, kidnappings and grenade attacks across Europe.
Europol urges early action to protect cryptocurrencies and sensitive data from quantum threats
The timing of these capabilities remains uncertain. However, this should not be the main concern. Adapting systems and coordinating security upgrades will take time. Therefore, regardless of the nature of the threats that may emerge, crypto-agility should be p
Ordering violence from abroad: five suspects arrested in Spain, Morocco, and France
Five suspects linked to the organisation and recruitment of serious violence have been arrested in Spain, Morocco, and France, in the latest results of the Operational Taskforce (OTF) GRIMM, coordinated by Europol. The arrests in August and September target th
Teenager suspected of leading KillSec ransomware group as law enforcement seizes servers and leak site
On 30 September 2026, law enforcement took control of KillSec’s leak site, securing at least 110 terabytes of data against further unauthorised access. The cybercrime group used the site to threaten organisations with the publication of stolen files unless the
Cannabis smuggling from North America and Thailand into Europe: Europol highlights growing threat
Cannabis smuggling from North America and Thailand in Europe has seen a sharp rise, driven by oversupply in legal markets and the adaptability of organised crime groups. A dedicated Europol Operational Taskforce (OTF) has been established to dismantle the crim
EU law enforcement chiefs gather to discuss new challenges in EU security
The Convention was opened by Jürgen Ebner, Europol’s Acting Executive Director, and Justin Kelly, Commissioner of the Irish An Garda Síochána.Jürgen EbnerEuropol Acting Executive DirectorOrganised crime itself has become digital by default. Technology is not j
Spain, Denmark and the Netherlands win Europol 2026 Excellence Awards in Innovation
At the European Police Chiefs Convention on 29 September 2026, Europol announced the winners of its 2026 Excellence Awards in Innovation. Law enforcement teams from Spain, Denmark and the Netherlands took home awards for projects that put innovation to work.
Protecting citizens, preserving rights
How can law enforcement make effective use of data and technology while ensuring that fundamental rights and the rule of law remain protected? This question was at the heart of the 17th Europol Data Protection Experts Network (EDEN) conference, held in Lisbon,
Six arrests for smuggling migrants via Schengen airports
Europol supported a migrant smuggling investigation involving law enforcement authorities from 17 countries. The criminal network was also engaged in document fraud and money laundering. The action day on 22 September 2026 in Austria, Italy, Spain, and the Uni
Donate to ICIJ
Support our journalism.
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet

The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousand are invisible to identity infrastructure by default, not because anyone hid th

Anthropic Cuts Live Internet Access for Internal AI Tests After Claude Exploits Injection Flaws
Anthropic on Friday said it's cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and targeted real websites. The AI company s

FBI Arrests Executive at Ransomware Negotiation Firm
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thousands of

ASOS Breach Reveals the Risks in Customer-Facing SaaS
The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network.

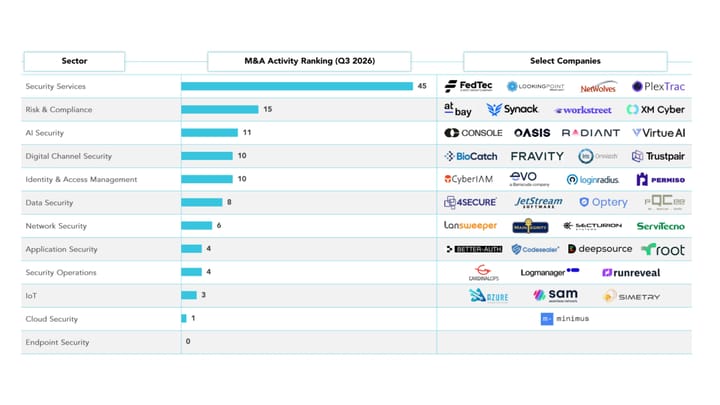
AI Scramble Drives Cybersecurity M&A Boom
Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What's different: Many of the buyers are not your typical cybersecurity firms.
Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories. "Using the account of Takashi Kitao, author

Japan confirms arrest of Russian Qilin operative, extradition to Germany
Japan’s National Police Agency confirmed the arrest and extradition to Germany of a Russian national accused of being involved in the Qilin ransomware gang.
FBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in September it had breached the FBI's jobs portal and stolen sensitive data on almos

What We Missed: FBI Strikes Back at ShinyHunters
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the arrest of a suspected ShinyHunters operative to the compromise of a Pentagon-run data center.
Security Threats Don't Stop at the Office: Why Executives' Families Need Training, Too
Those closest to executives must match their security postures because the weakest link in a family can become the entry point for attacks.
Hundreds of thousands impacted by data breach at biosensor firm iRhythm
A company known for wearable cardiac sensors, iRhythm, has begun notifying states of the impact of a data breach from the summer.
Leader of vast money mule operation that laundered cybercriminal proceeds pleads guilty
Oleg Korniev, a 42-year-old dual citizen of Ukraine and Russia, was a principal of Your Mule Cashout, or “YMCO,” which from 2007 until 2014 set up a sophisticated network of mules in the U.S. and Europe.
FBI touts another ShinyHunters arrest in response to data breach
“We will continue to work closely with our partners to disrupt what’s left of the ShinyHunters group and their associates, no matter where they operate," FBI Director Kash Patel said.
Belarusian hacktivists admit to 2023 breach of Russian state healthcare network
The Belarusian Cyber Partisans concurred with Russian research that they indeed spent months inside the network for the Moscow Department of Health.
$10 million bounty offered for Chinese Hafnium hacker accused of Microsoft Exchange Server mega-attack
The US State Department is offering up to US $10 million for information about the whereabouts of Zhang Yu, a 44-year-old Chinese national who is accused of being a key figure in China's state-sponsored hacking group, Hafnium. Read more in my article on the Ho
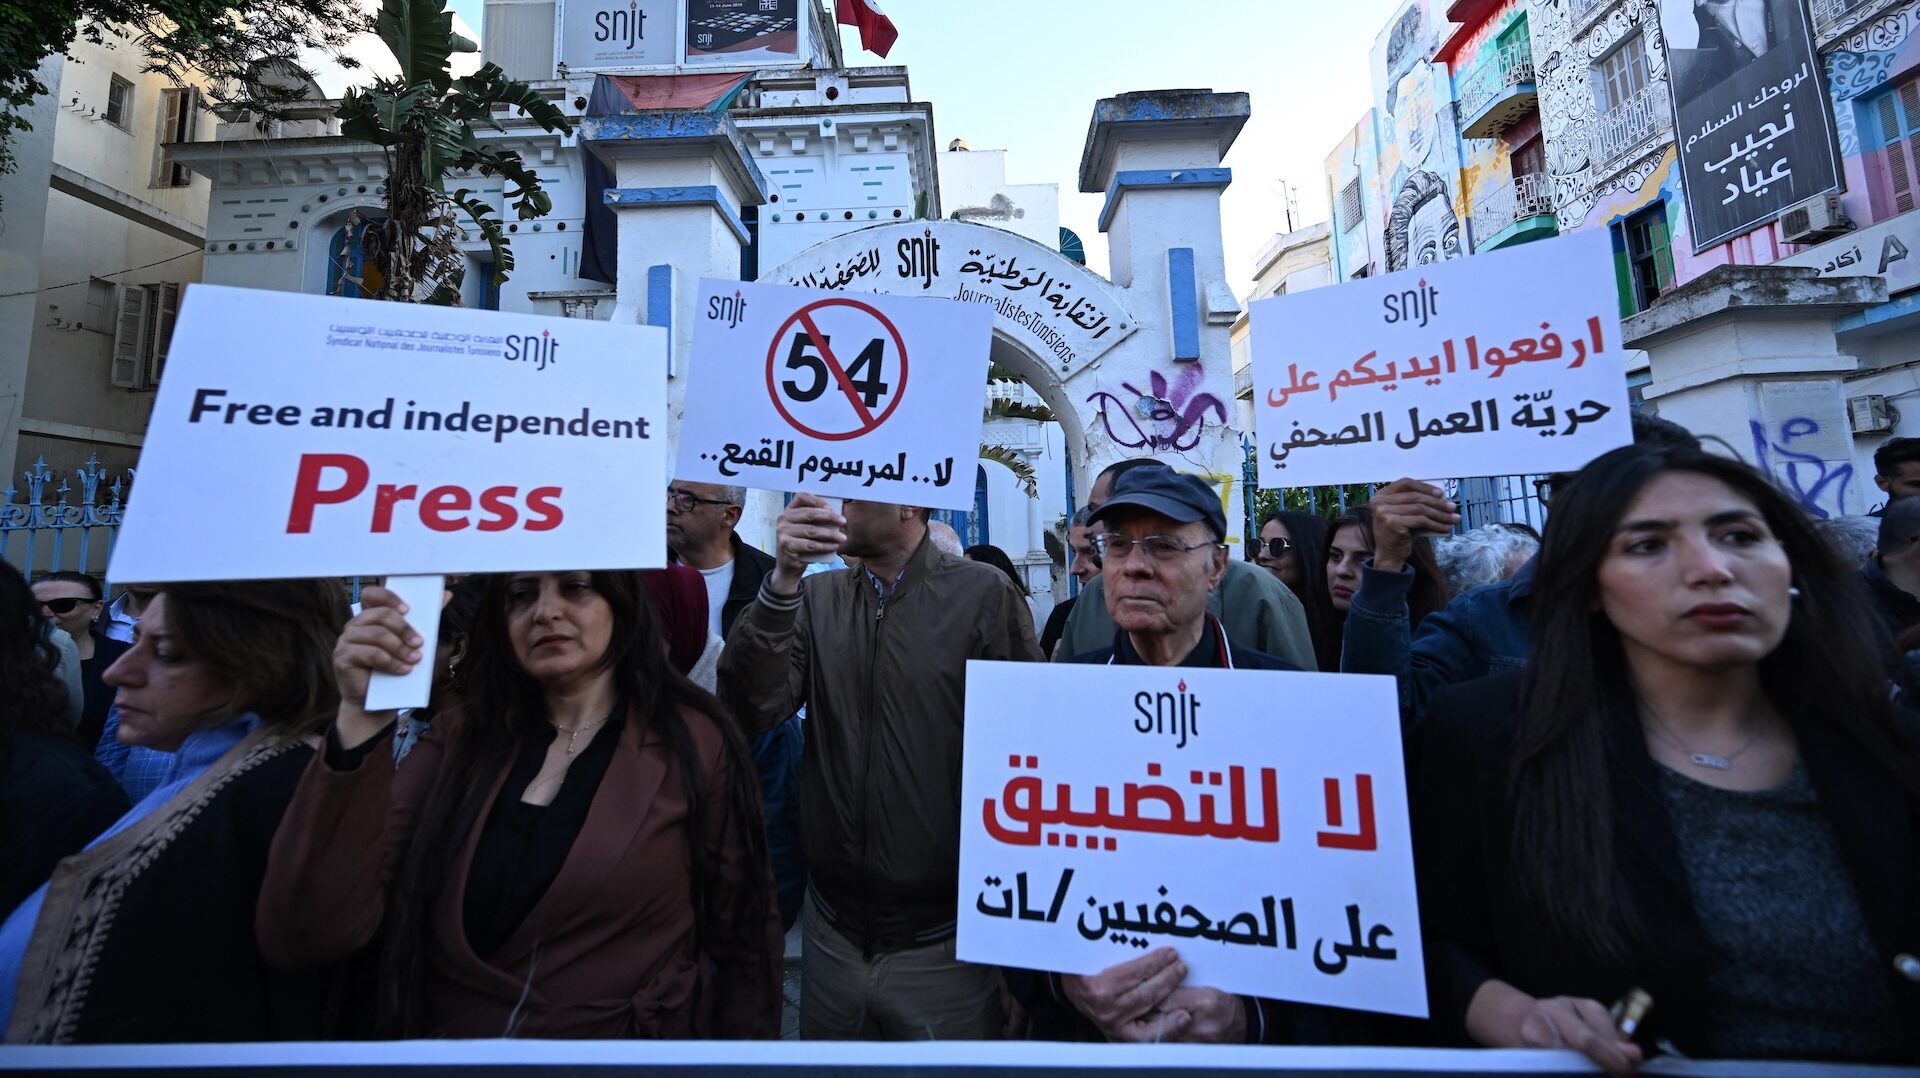
Tunisian court dismisses case to dissolve publisher of ICIJ partner Inkyfada
Despite the court victory, Inkyfada and its parent company Al Khatt still struggle to recover funds frozen by authorities.
TP-Link Sued by Four More U.S. States Over Router Security and China Ties
Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers are and how sep

Social Engineering AI Agents: The New BEC for 2026
As AI agents gain authority over business systems, attackers can manipulate them like business email compromise (BEC) victims.
Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its c

Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). "It's an opt-in service informed by our experience using Claude to find vulnerabilities during Project Gl

Attackers Exploit AhsayCBS Flaws to Deploy XMRig Miners Disguised as Microsoft Edge
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below - CVE-2026-105133 (CVSS v4 score:

Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in ques

The AI Velocity Paradox: Why Security Is Decades Behind AI Ambition
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The "Horizons of Identity Security" report from SailPoint highlights a critical “velocity par

ASOS breach update: Hackers stole customer details and shopping searches
Stolen ASOS data includes shopping searches as well as personal details, so customers should watch out for convincing phishing messages.
GoBalance Flaw Lets Attackers Hijack .onion Addresses by Recovering Tor-Format Keys
A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a site's .onion address using only public information, and then take that address over. Searchlight Cyber, which disclosed th

'AgentCorruption' Puts AWS Environments at Risk With Single Prompt
A now-patched vulnerability in AWS Bedrock AgentCore could have allowed an attacker to use one AI chatbot to take over an organization's entire fleet.
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpotting
The first cybercriminal to ever make the FBI's "10 Most Wanted Fugitives" list allegedly infused Tren de Aragua's violent criminal operations with cash.
Russian Spies Give 'MatchBoil' Malware a Stealthy Facelift
Cyber-espionage actor UAC-0099 has been steadily refining its flagship dropper in campaigns targeting Ukrainian organizations.
Attackers hijack country-code domains to impersonate Google and other services
Cybercriminals compromised three country-code namespaces to get certificates that could help them impersonate trusted sites.
Five years after the Pandora Papers, transparency laws lose their teeth
Reforms promised swiftly after ICIJ’s investigation have fallen short in New York and beyond.
Amazon has an uncomfortably personal profile on you
Amazon thinks it knows your body, your family, and your life. You didn't sign up for it, and we couldn't find a way to opt-out.
Writing the Next Chapter
Dark Reading is about to begin a new decade in its storied history, and we have some breaking news of our own to share.
Meta’s Muse AI files away your friendships, arguments, and secrets
Meta’s Muse AI builds personal dossiers that would make the FBI jealous. Even people who never signed up can get caught in its files.
Smashing Security podcast #487: Clippy’s crypto comeback
Microsoft's Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn't from Microsoft either. Meanwhile, UK losses from hacked email
Australian Gov't Weighs Mandatory AI Incident Reporting
In the wake of an agentic attack against its own Medicare systems, Australia's government is feeling out what regulations might look like for frontier AI companies.
How Hungary’s richest man funneled millions into Orbán’s propaganda machine
Since 2022, companies belonging to Lőrinc Mészáros, who amassed a fortune from government contracts, donated more than $13 million to an online mouthpiece of the Fidesz party, a new Direkt36 investigation reveals.
ShinyHunters Extorted Boeing Spin-off Prior to Arrests
A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of the hacking gang. KrebsOnSecurity has learned that the suspect

Google issues Android security updates: who can get them and how
Google has new Android updates, but many users will not be able to get patched immediately.
AI-powered phishkit arms criminals with account-hijacking tools in 10 minutes
BlueKit puts account-hijacking tools in more criminals’ hands, making it easier to target you with convincing fake login pages and scam messages.

Update Chrome and ChromeOS to fix critical security issues
Google has released a new update for the Chrome browser and ChromeOS. There are a lot of security fixes in them so don't delay.
Another ShinyHunters suspect arrested
The net is tightening around the Shiny Hunters cybercrime group following the reported arrest of a second member.
Did someone share an explicit image of your child online? Take these steps
Did someone share an explicit image of your child online? Possessing or sharing explicit images of children can be a serious crime — and that includes AI-generated deepfakes. Report the perpetrator immediately to criminal law enforcement and take action to get
Groups Associated With India’s Far-Right Receive Millions Through US Donor-Advised Funds
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published. US non-profits whose founding leaders or organisations have been associated with India’s controversial Rashtriya Swayamsevak Sangh (RSS) – or initiatives the Hi
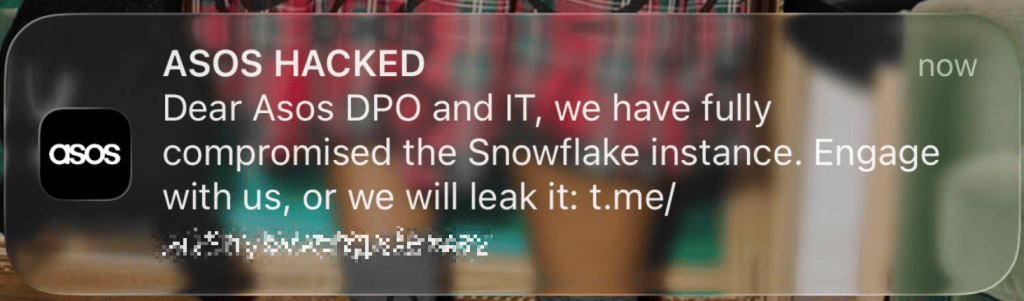
ASOS “hackers” send push notifications to customers
ASOS customers received a push notification regarding a breach of the company. Here's what we know so far.
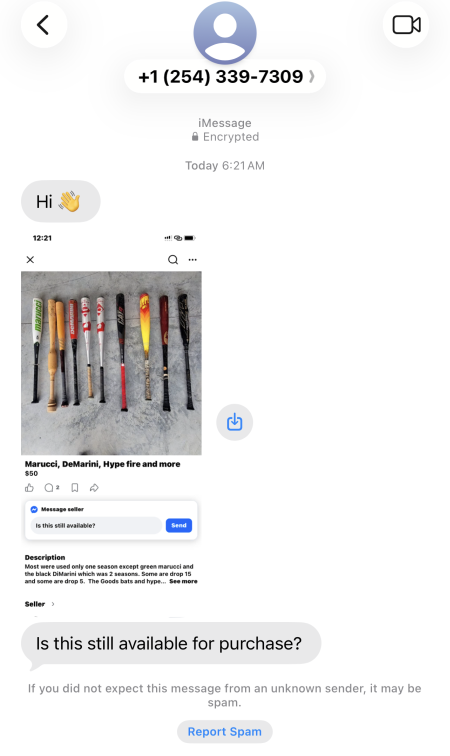
Facebook Marketplace scam uses your name and number
Facebook users are reporting receiving a message with a fake Facebook Marketplace listing that has their name as the seller.
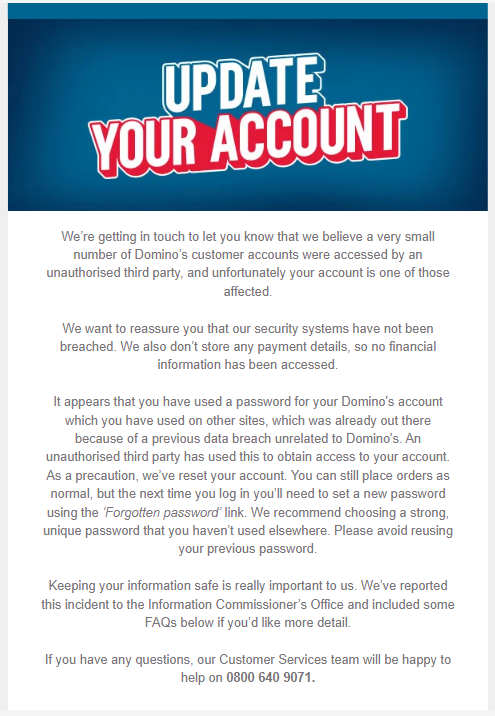
Domino’s customers targeted in credential stuffing attacks
Domino's is warning customers by email that their accounts have been compromised in a credential stuffing attack.
Google pauses open source bug bounty program after rise in AI submissions
Google has frozen its OSS VRP product vulnerability submissions to stop the flood of AI generated vulnerability reports.
Proposed anti-Flock bills could spell trouble for license plate readers
Two sets of US lawmakers introduced bills in late September and early October to tackle the growing concerns about automated license plate readers.